Offensive security for web apps and APIs
Find the vulnerabilities others miss.
Researcher-led security testing for web applications, APIs and email domains.
“It was of great support to us, highlighting weaknesses in our system. He always behaved as a professional, it has been a pleasure to work with him.”
“Muhammad identified vulnerabilities on our website that we were unaware of, and his work was crucial in helping us improve our website’s security.”
“I had the pleasure of collaborating with Muhammad and was impressed by his exceptional skills, professionalism, and integrity.”
Vulnerabilities acknowledged by
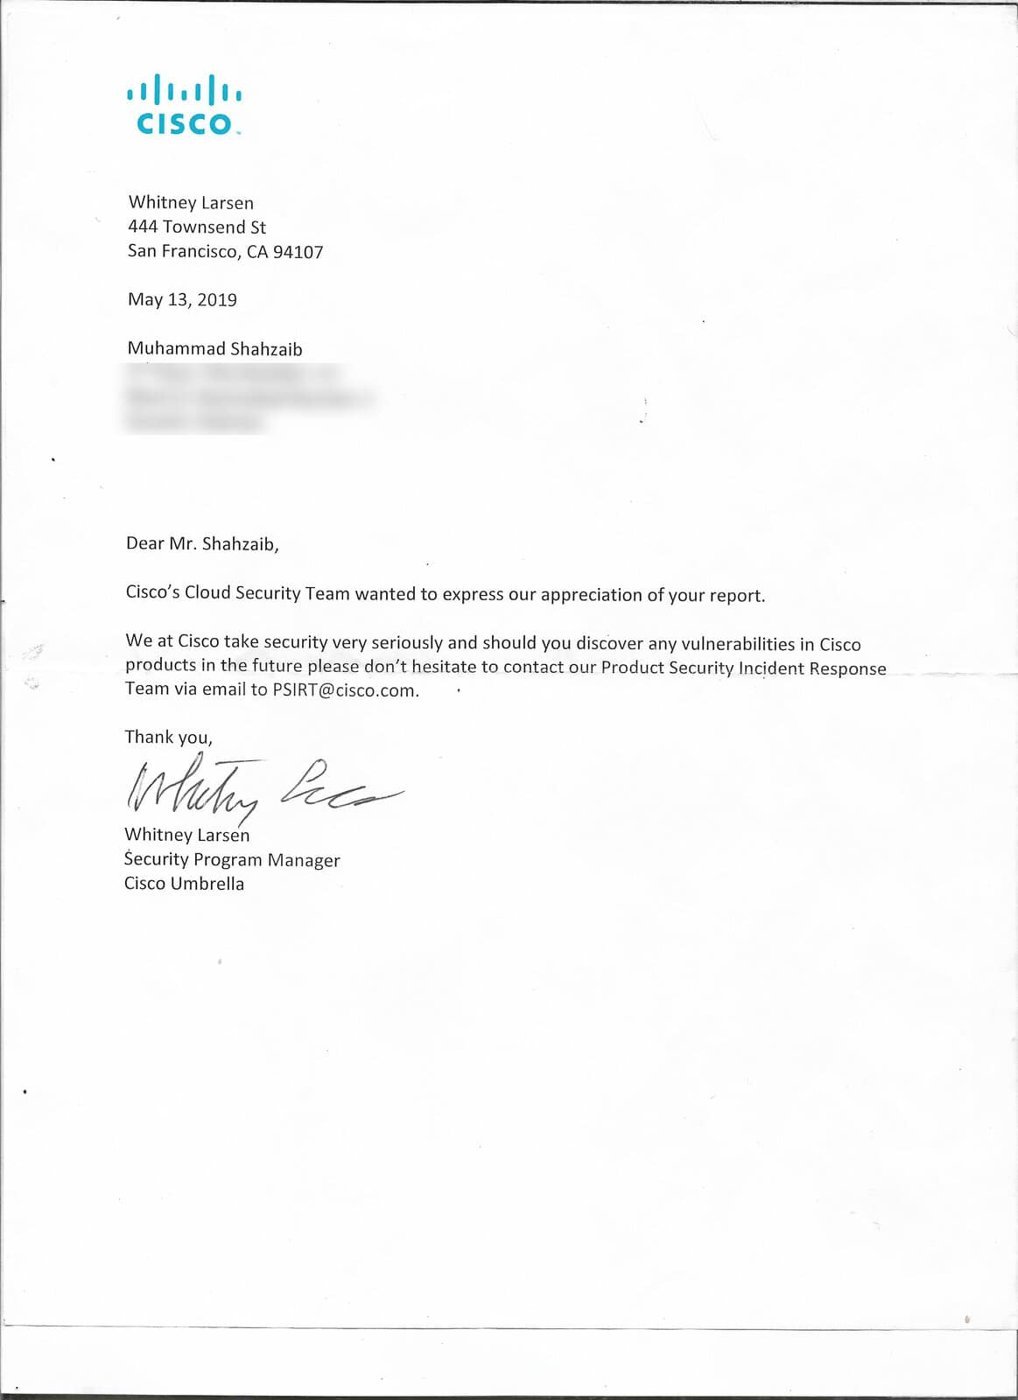
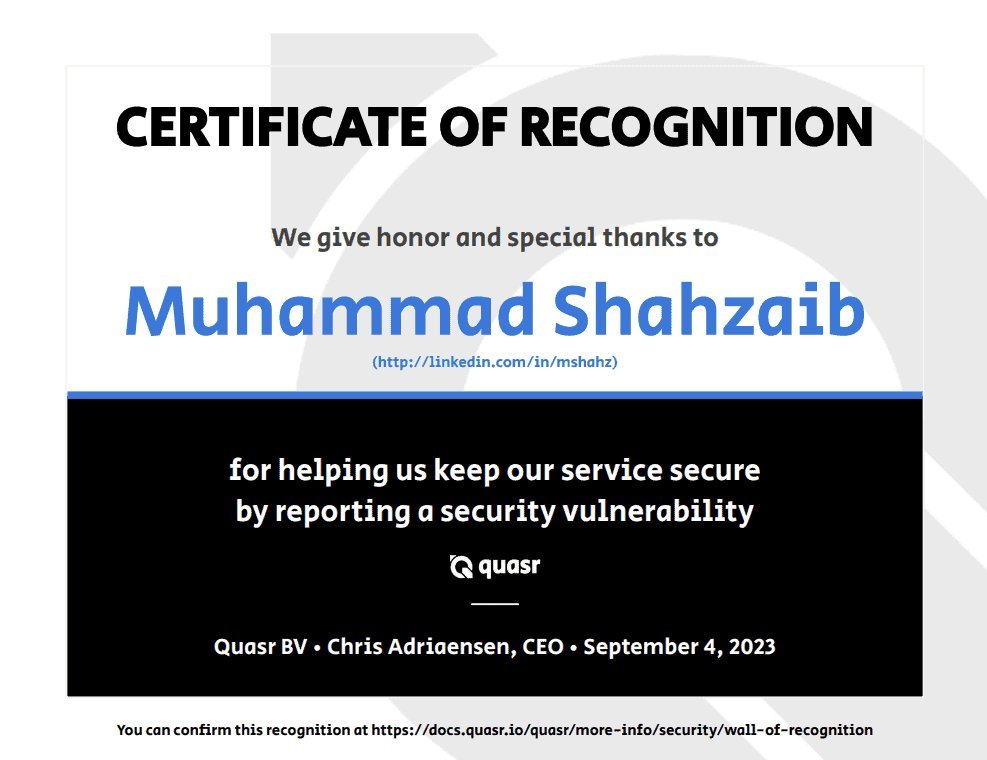
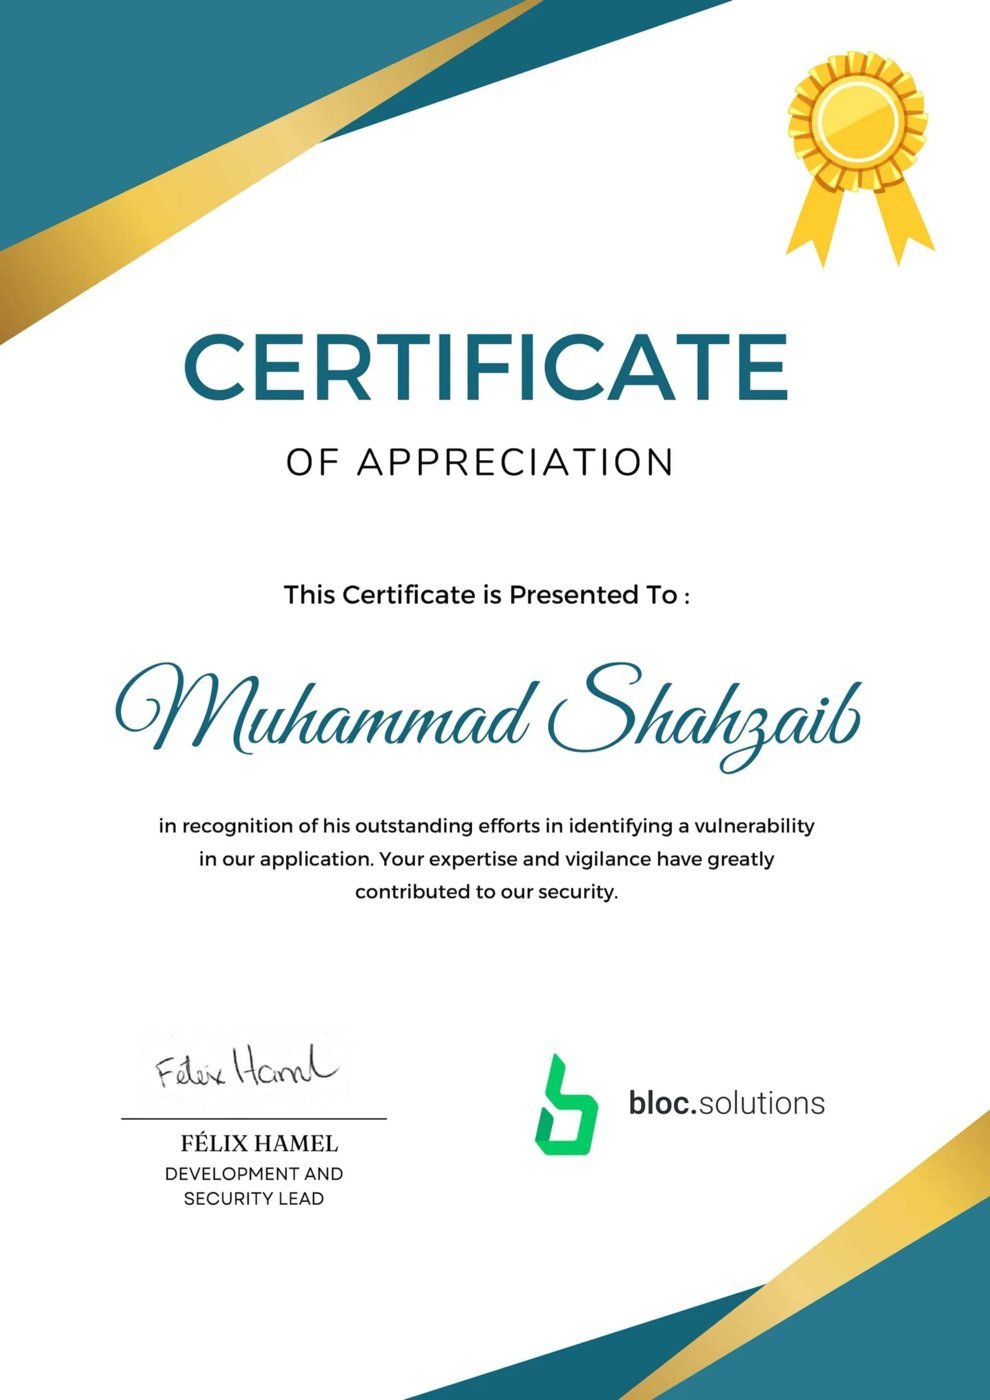
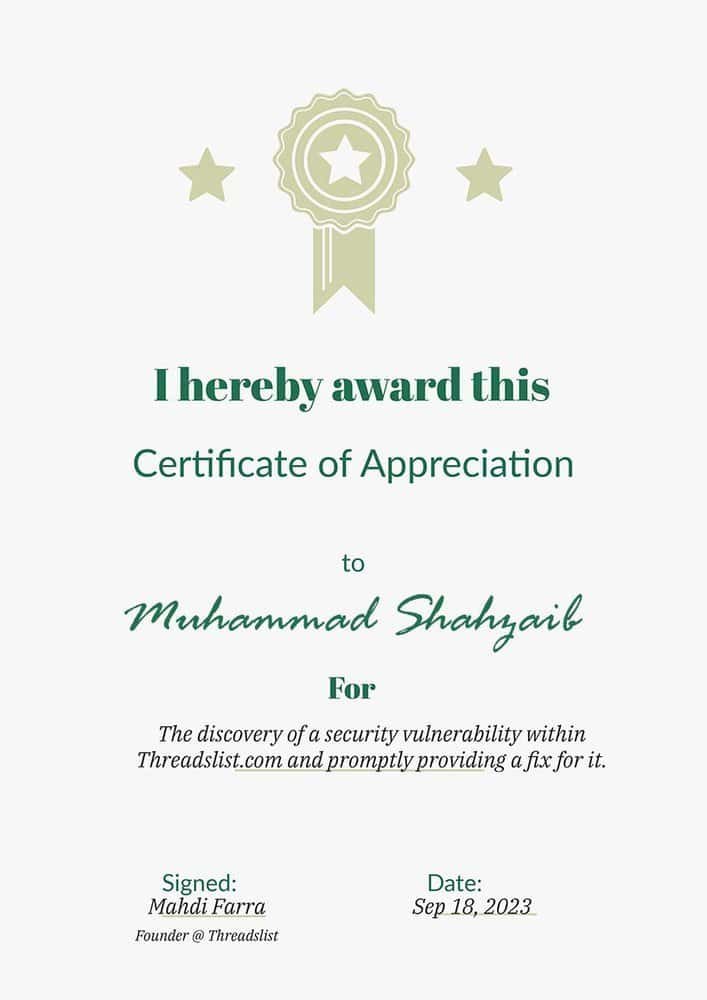
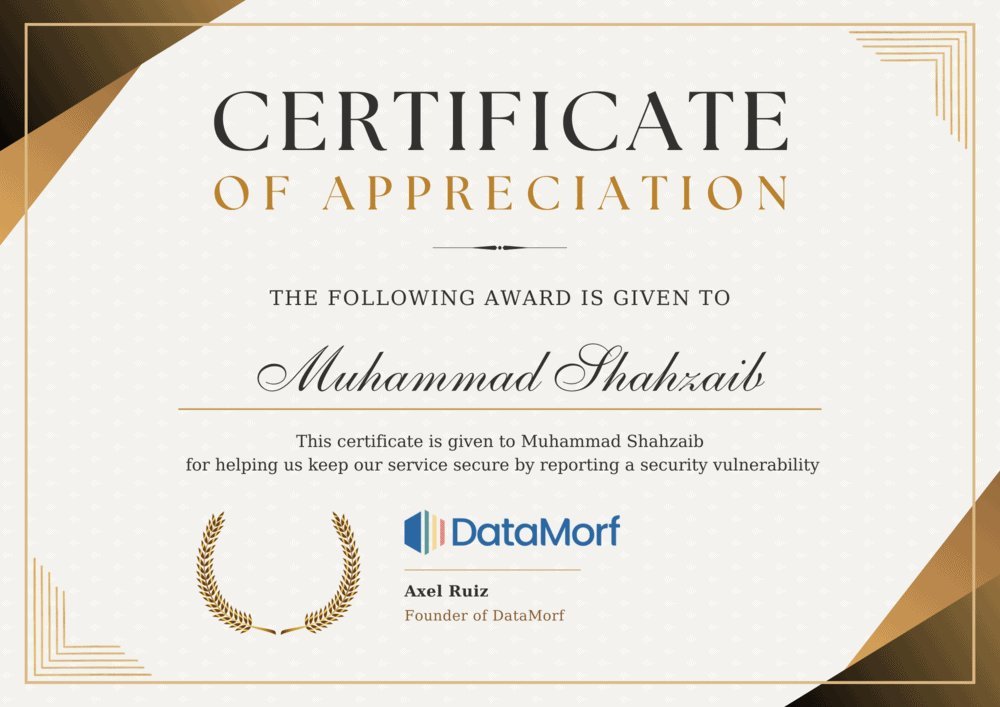
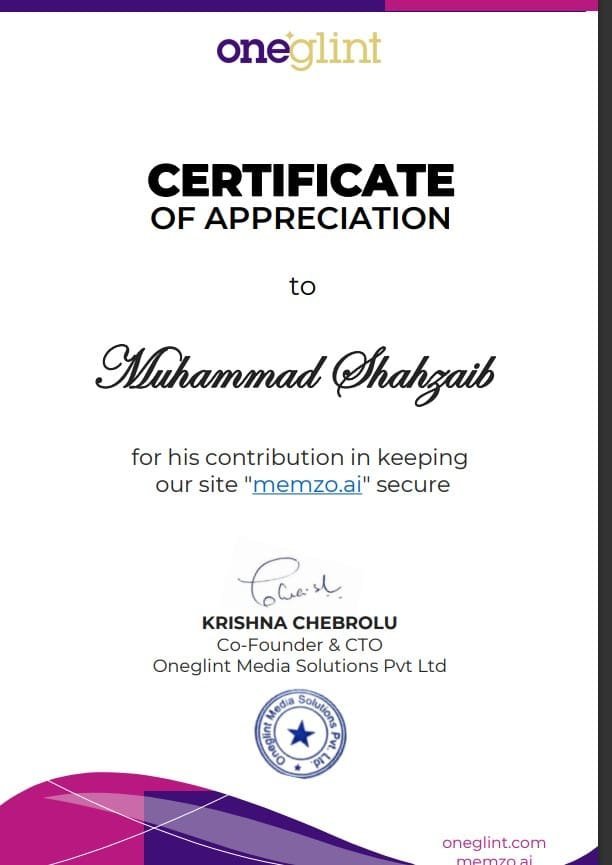
Click a logo to view the acknowledgement.
Proof
Trusted by the people who fixed what we found.
Recommendations from founders, engineers and security leaders, published with their permission.
About
Built by a researcher, not a sales team.
Alcyne Tech is a web security firm led by Muhammad Shahzaib, a security researcher who has been finding and responsibly reporting vulnerabilities since 2018, with acknowledgements from companies around the world.
Behind every engagement is a small team of expert security researchers who test the way real attackers think: by hand, with care, and without shortcuts. We keep the team deliberately small, so the people who scope your project are the same people who test it and explain the results.
Our work is simple to describe and hard to do well: find what others miss, explain it in plain language, and give your team clear steps to fix it.
Beyond the surface
Scanners find the obvious. We find what they miss.
Automated tools check for known patterns. Attackers don’t. They chain small flaws, abuse business logic and pivot through the trust between your systems. That’s where we spend our time.
Tested by hand
Every target is worked by a researcher who thinks like an attacker, not a tool that matches patterns.
Findings, chained
Low-severity issues rarely stay low. We show how small flaws combine into real compromise.
Impact before jargon
Each finding explains what an attacker could actually do to your business, then how to stop it.
Services
Security testing, scoped to what matters.
Start with a free check. Go as deep as your risk requires.
Free security check
Free
Find out where you stand before someone else does.
- TLS and certificate review
- Email domain configuration check
- DNS and domain hygiene
- Top-line findings by email
Essential Defense
$500
Lock the front, back AND the side door.
Send cold emails? We help them avoid spam while making your domain more secure at the same time.
- SPF, DKIM and DMARC review with a step-by-step enforcement guide, plus 1 month monitoring
- Security headers reviewed
- TLS configuration reviewed
- CORS policy review
- Broken link hijacking check
- Subdomain takeover and exposed files check
- Written findings with steps for the fixes
Most thorough
Web Application Security Review
$1,500
The testing automated scanners only dream of.
Scoped for one web application or MVP: up to 2 user roles and its main API.
- Everything in Essential Defense, plus:
- Authentication and session handling
- Session and cookie security: logout invalidation, expiry, secure flags
- Access control and IDOR
- Injection: SQLi, XSS, SSRF and more
- Unrestricted file upload testing
- Sensitive data exposure
Further testing
APIs, multiple applications, cloud exposure or ongoing testing.
Larger and custom scopes are quoted individually, after a short call.
All active testing runs under written authorization and agreed Rules of Engagement (RoE), with a mutual NDA available on request. Nothing destructive is ever run against production without your explicit approval.
How it works
From first look to confirmed fix.
01
Free check
A passive look at your exposure. Nothing accessed, nothing kept.
02
Scope and authorize
We agree on targets and depth in writing before any active testing.
03
Test and report
Manual testing, then a clear report: impact, proof and fixes.
04
Fix and verify
Your team applies the fixes using our steps. We verify them to confirm the issues are closed.
For agencies and dev teams
Ship code that’s secure before it goes live.
We work alongside agencies and development teams as an extra set of attacker’s eyes. Before launch, after major releases, or whenever a client asks how secure their product really is.
- Security testing before launch
- Reviews after major releases
- Clear findings your developers can fix fast
- Flexible engagements for client work
Why Alcyne Tech
Quiet, careful, thorough.
Researcher-led
Experienced researchers, hands-on. Vulnerabilities acknowledged by companies worldwide.
Clear pricing
Fixed prices for defined scopes. Custom work is quoted upfront.
Authorized only
No active testing without written authorization from the site owner.
Confidential by default
Findings go to you and the people you name. Nobody else.
Plain-language reports
Business impact first, then exactly how to fix it.
Proof of coverage
Every test case documented, with its outcome, in your Test Coverage & Verification Report.
FAQ
Questions we get asked.
Will testing disrupt my site?
The free check is passive: it reads public records and the responses your site already sends to every visitor. Active testing is scheduled with you, agreed in writing and run carefully to avoid disruption.
Do you need access to my systems?
Not for the free check. For deeper testing we agree on scope first, and some tests use test accounts you provide. Nothing is touched without your written authorization.
What do you test beyond websites?
APIs, multiple applications, cloud exposure and email domains. Larger or custom scopes are quoted individually.
What if our application is already well-secured?
Every application review delivers a full Test Coverage & Verification Report. Even if no critical vulnerabilities are present, we document every authentication flow, endpoint and logic layer tested, with clear fix steps for anything worth improving. You walk away with concrete evidence of testing to share with customers, partners or investors.
Can I fix the issues myself?
Yes. Every finding comes with clear fix steps. Fix it in-house, hand it to your developer, or ask us to help.
Are my findings kept confidential?
Yes. Findings are shared only with you and the people you name. They are never published or used in our marketing.
Do you work with agencies and dev teams?
Yes. We work alongside agencies and development teams on pre-launch testing, reviews after major releases and ongoing client work. Get in touch to discuss what fits.
Who does the testing?
A small team of experienced security researchers, led by Muhammad Shahzaib. Every engagement is tested by hand and supported by advanced tooling.
Get started
Start with a free security check.
Send us your website. We’ll take a passive look at your exposure and reply with what deserves attention, in plain language.
- No access to your systems, no data kept
- Clear findings, no jargon
- No obligation
Agency or larger scope? Tell us in the form and we’ll follow up with details.
Prefer email? info@alcynetech.com
Request your free check
Offensive security for web applications, APIs and email domains. Researcher-led, authorized testing only.
© 2026 Alcyne Tech. All rights reserved.
Active testing is performed only with written authorization.